Technology
CISA, FBI, HHS, USDA and DOT warn of attacks on supermarket and cold-storage refrigeration controllers
CISA, the FBI and the US health, agriculture and transport departments urge critical infrastructure operators to harden industrial refrigeration and cold-chain monitoring systems that are being targeted by cyberattacks.
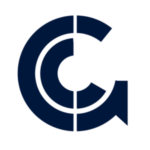
The controllers that keep the right temperature in supermarket refrigerators and in food cold-storage warehouses have become targets of cyberattacks. On Thursday, November 5, 2026, CISA (the US Cybersecurity and Infrastructure Security Agency), the FBI and the departments of Health (HHS), Agriculture (USDA) and Transportation (DOT) issued a joint announcement urging critical-infrastructure operators to harden industrial refrigeration and cold-chain monitoring systems.
The agencies say malicious actors are targeting electronic temperature controllers and commercial refrigeration controllers that are unpatched or exposed to the internet, in food retail stores and cold-storage warehouses around the world. These devices are also widely used in other sectors: Healthcare and Public Health, the chemical industry, Food and Agriculture, and Transportation, which includes refrigerated transport.
What can happen in practice
What can happen in practice is explained in the agencies’ accompanying fact sheet. Attackers exploit authentication bypass, arbitrary code injection and weak configurations, and can force units to run continuously in heating and defrost cycles. The temperature swings shorten the life of the equipment, create a fire risk, cause loss of goods and can indirectly harm consumers who eat food stored unsafely. At the same time, operators may lose sight of the real temperature.
Chris Butera, acting executive assistant director for Cybersecurity at CISA, urged organisations to assume they may be targets and to study the fact sheet. Brett Leatherman, assistant director of the FBI’s Cyber Division, said such systems are being attacked in critical-infrastructure sectors around the world and urged that the measures be applied and any suspicious activity reported to the FBI.
The measures recommended
The proposed measures are aligned with the Cross-Sector Cybersecurity Performance Goals of CISA and NIST, the US national standards body. The agencies ask for the following:
- Remove exposure to the public internet, especially of the controllers’ control panels, and, if remote access is needed, protect it with an up-to-date firewall or perimeter device.
- Isolate operational technology (OT) devices on a separate virtual network (VLAN) from the business network.
- Change default passwords, strengthen password policy and, where possible, use phishing-resistant multi-factor authentication.
- Apply security updates and replace devices no longer supported by the manufacturer.
- Restrict access with allow-lists of devices and IP addresses.
- Keep reliable backups, stored offline and off site and tested regularly.
- Keep event logging with regular review; where devices do not keep the usual logs, record network traffic.
- Set reasonable limits on device setpoints and receive an alert on any deviation.
Not a new issue
The subject is not new for CISA. In December 2020, as the distribution of coronavirus vaccines was being prepared, the agency issued a guide titled “Cold Storage Cyber Custodial Care”, in which it noted that malicious cyber actors had shown interest in the IT systems supporting the vaccine cold chain. The guide recommended, among other things, that the systems not be visible to connected-device search engines such as Shodan and Censys, and that a second, less exposed thermometer be kept for independent verification.
A little earlier, on Wednesday, November 4, the European agency ENISA and the Commission had warned of attacks on refrigeration systems in EU member states, so the problem is not limited to the US. Anyone who detects suspicious activity can contact CISA’s 24/7 operations centre ([email protected], 1-844-729-2472), the FBI’s Internet Crime Complaint Center (ic3.gov) or a local FBI office. For impacts on the health supply chain, HHS accepts reports at [email protected].